
Gigabyte Control Center kernel vulnerability patched; update required
Gigabyte has addressed a critical security flaw in its Control Center software that allowed attackers to bypass memory protections and gain kernel-level access on affected systems. Users should update immediately.

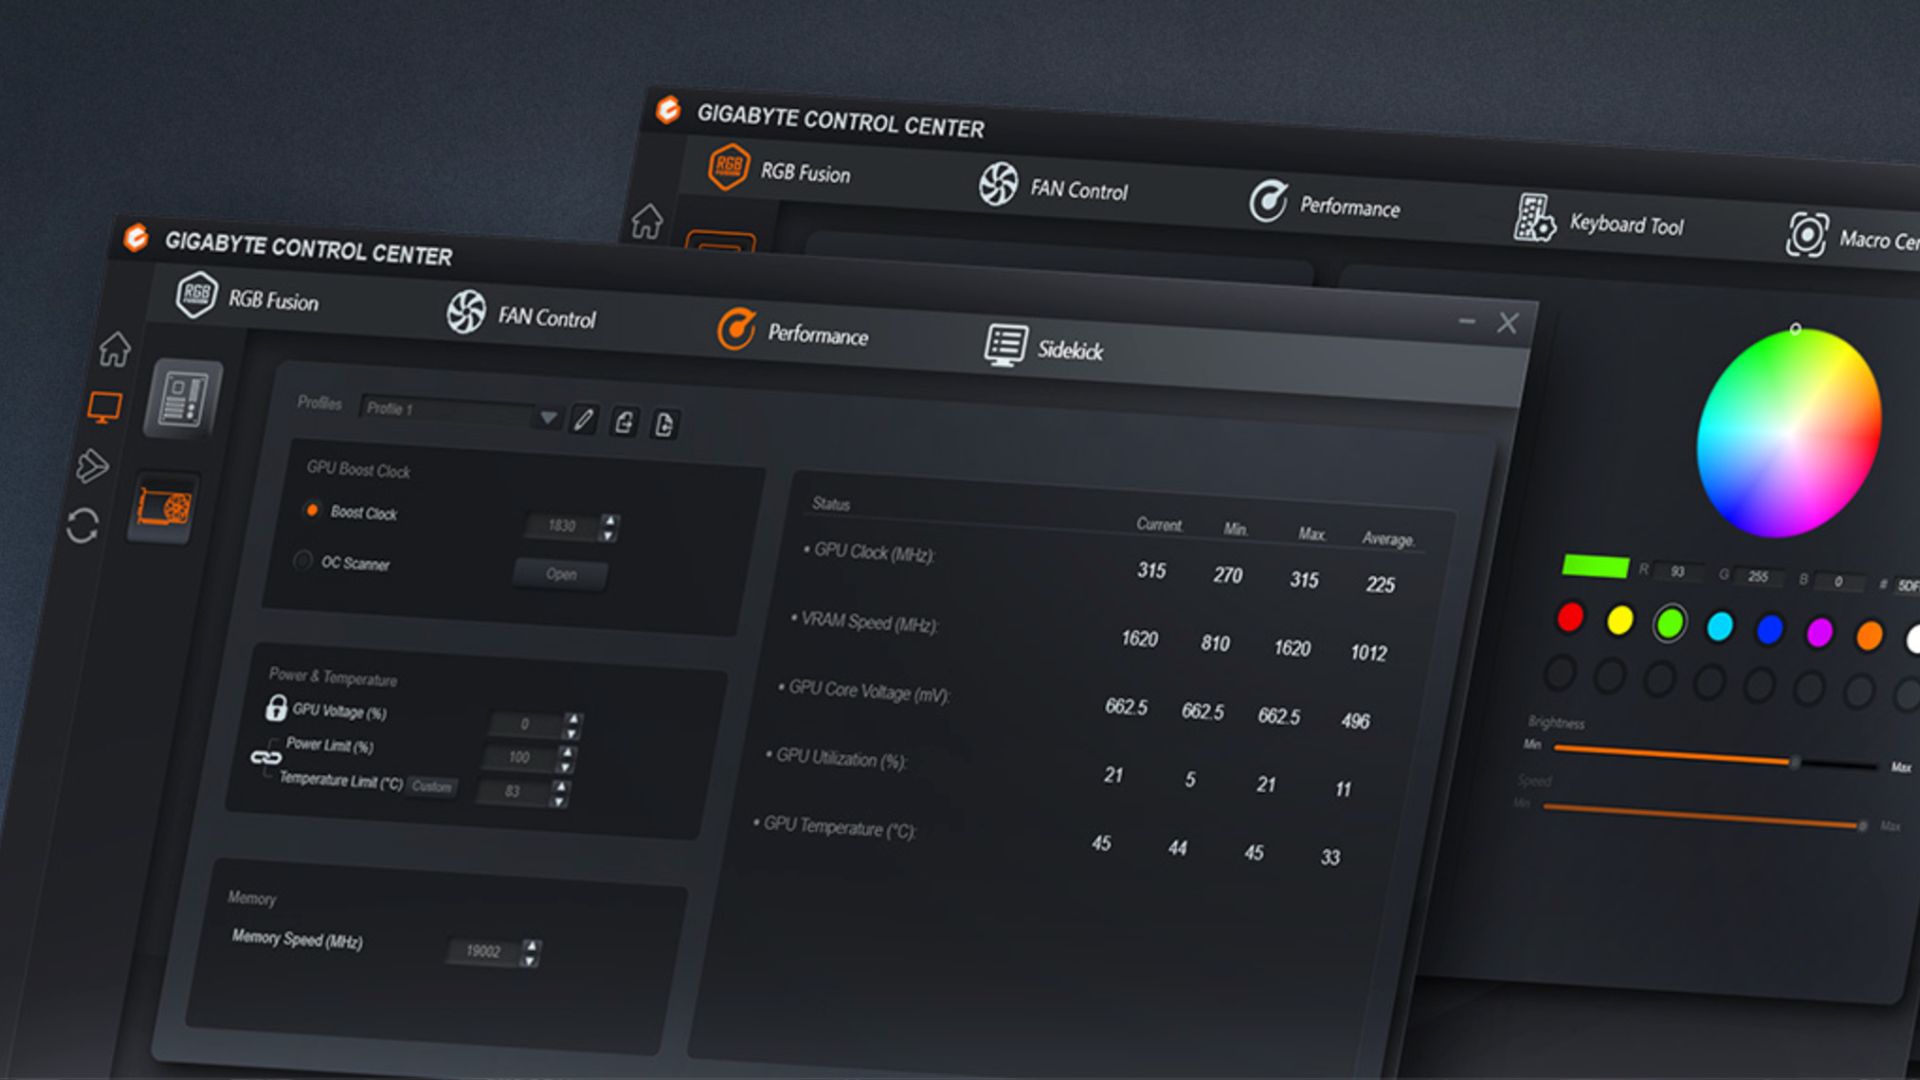
Gigabyte has disclosed a vulnerability affecting kernel drivers in its Control Center (GCC) software, which ships alongside many of the company's motherboards. The flaw exists in two drivers, GVCIDrv64.sys and gdrv3.sys, and could allow local attackers to escalate privileges to kernel level.
The vulnerability stems from insufficient access control and improper validation of input parameters in the drivers' IOCTL interfaces. An attacker with local access could send a specially crafted IOCTL request to bypass memory protections, gain direct hardware access, and elevate themselves to kernel privileges, the highest access level on a PC.
Gigabyte has released patched versions addressing the issue. Control Center version 26.09.10.01 and later includes the fix, as do versions GBT_VGA_26.08.24.01 and GCC 26.08.28.01 or newer. The mitigation involves enhanced access control with strict security descriptors, removal of unnecessary high-risk interfaces, mandatory privilege validation for hardware access functions, and rigorous input validation for all IOCTL parameters.
The company credited researchers Mohamed Alzhrani and Subhan Sultanov for discovering the vulnerability and assisting with the patch. Users with Gigabyte motherboards should download the latest version of Control Center from Gigabyte's website.
Sources
- PC GamerEstablished publication · recorded Sep 22, 2026Gigabyte admits an oopsie with Gigabyte Control Center software leaving kernel exposed to attackers